
802.1X Cloud Ready
Unify Zero Trust Network Access and start to secure all devices and users with Cloudi-Fi
Cloud-native identity-based access control
No local Radius servers needed
The Cloudi-Fi Cloud Network Access Platform can now secure complex organisations’ Guests, BYOD, IoT, and employees.
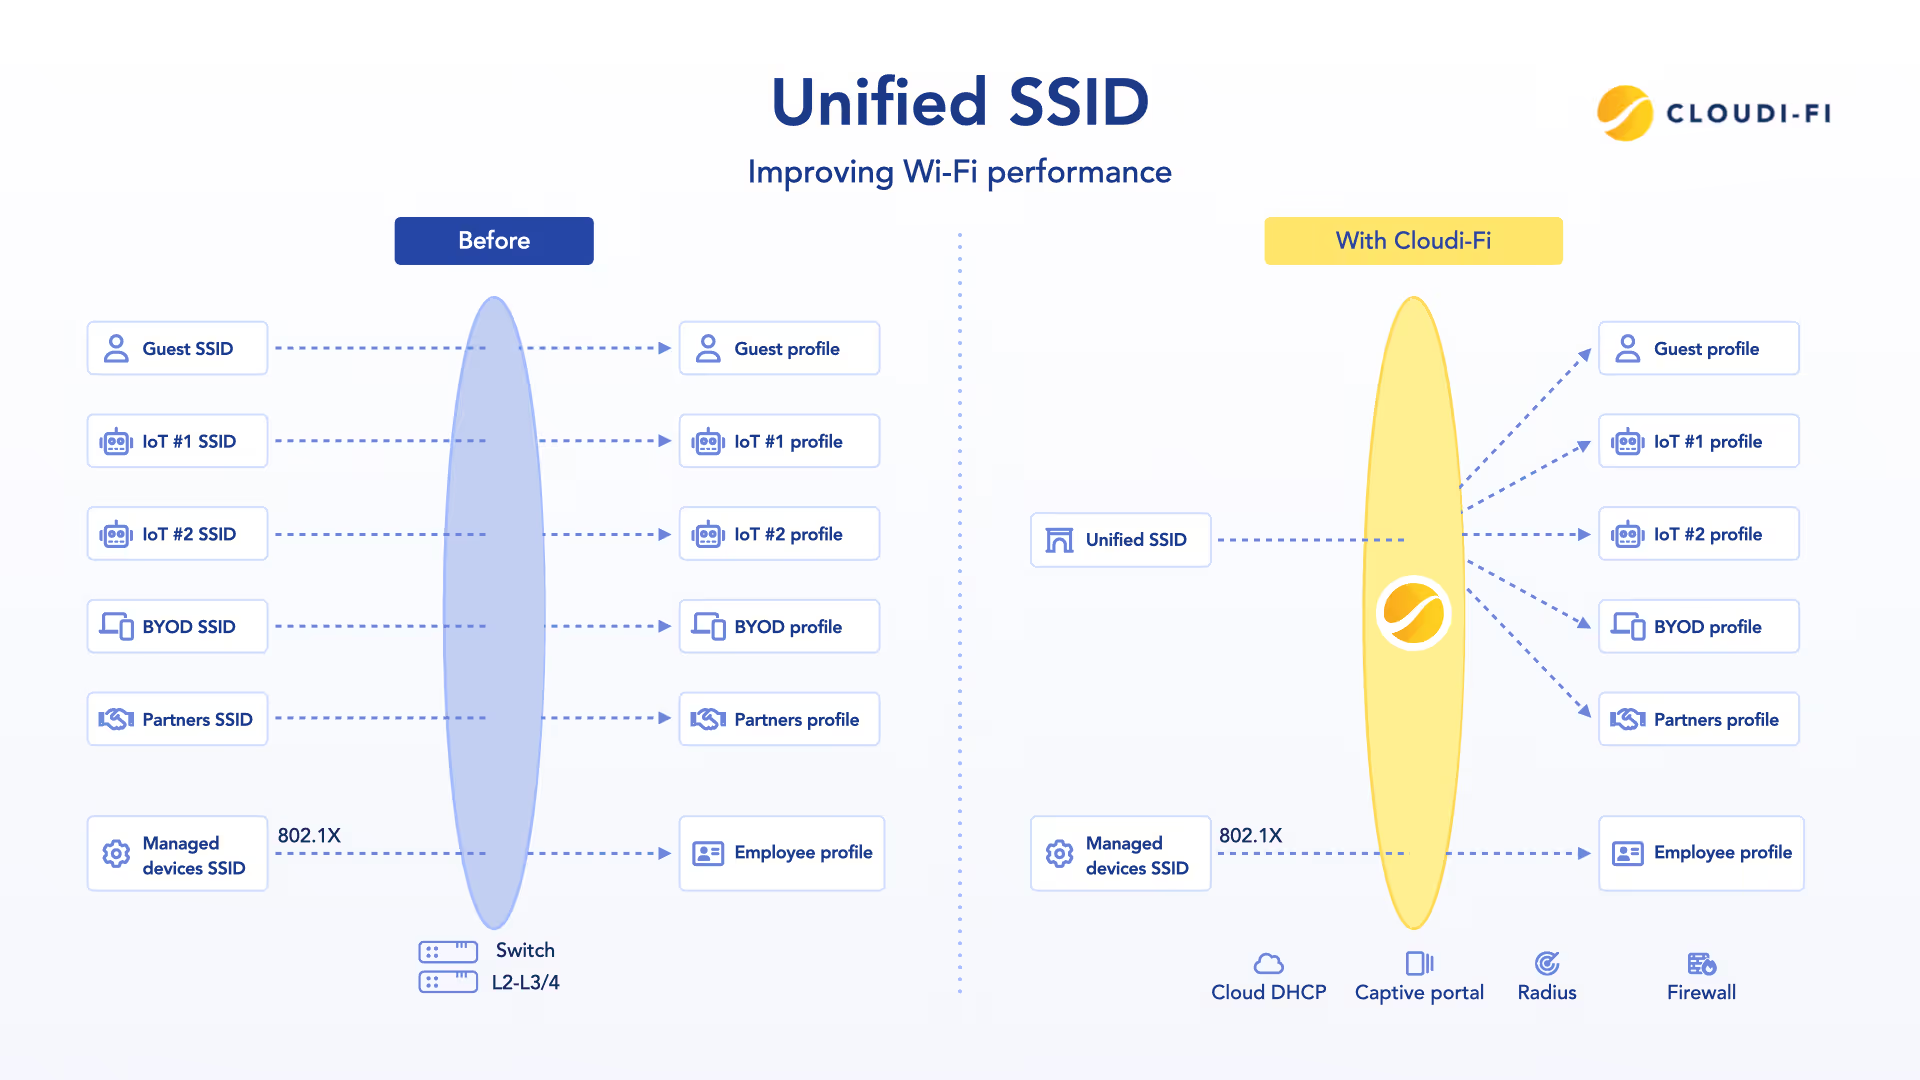
802.1X provides identity-based access control to your network. With Cloudi-Fi, you gain a cloud-native solution that integrates easily with your existing infrastructure — no local RADIUS servers or complex setups required.
Key benefits
- Strong, identity-based authentication
Every user or device must prove their identity before accessing the network (via certificates, credentials, etc.). - Fully cloud-managed
Cloudi-Fi handles all authentication flows without requiring on-prem infrastructure. - Ready for Zero Trust
Enforce micro-segmentation and role-based access at the network level.

Supported 802.1X authentication methods
Cloudi-Fi supports multiple authentication methods to adapt to your IT environment, whether you’re using cloud identities, on-prem directories, or certificates.
Certificate-based authentication (EAP-TLS)
Authenticate users or devices via digital certificates installed on endpoints.
- Seamless, passwordless user experience
- Secure identity validation with your internal certificate authority
- Ideal for managed environments with strict security policies
LDAP / Active directory integration
Authenticate users against your existing LDAP directory.
- Compatible with Active Directory, OpenLDAP, and more
- Identity-based access control with no infrastructure changes
Microsoft Entra ID (formerly Azure AD)
Leverage your Microsoft 365 credentials for secure, cloud-based access.
- Native integration with Microsoft Entra ID
- Federated authentication and central identity management
- Perfect for hybrid or fully cloud-based environments
MAC-based authentication
Identify and control access for non-user devices that can’t support credential-based authentication.
- Useful for IoT, printers, and legacy devices
- Access restrictions via VLANs or tailored policies
- Works as a fallback or in parallel with user-based authentication
Zero Trust Network Access
Aligning with Zero Trust principles, Cloudi-Fi ensures that every device and user is authenticated and verified before granting access. This approach minimizes potential security risks associated with unmanaged devices and open networks.
Seamless integration with existing ecosystems
Cloudi-Fi integrates smoothly with various network infrastructures, including Cisco WLC and HPE Aruba Networking. These partnerships enhance the capabilities of existing hardware, providing customizable, secure, and compliant guest Wi-Fi and BYOD solutions without the need for additional hardware investments.
Identify・Secure・Automate
Cloudi-Fi helps global organizations unlock their Universal ZTNA strategy


Start your journey with Cloudi-Fi

Instant, secure access to everything, anywhere
One solution for heterogeneous technology platforms and vendors
Integrated with the best technologies on the market
Infrastructure agnostic and plug-and-play deployment: rapidly roll-out Cloudi-Fi across global sites with any infrastructure provider
Cloud native, borderless, scalable and global!
Unlocking Universal Zero Trust Network Access on all continents

One platform for all industries
Cloudi-Fi empowers organizations with a scalable, cloud-based solution to secure users, devices, and data. Designed to integrate seamlessly into existing infrastructures.
